COSGrid TrustShield AI | AI Usage Control

Discover AI Apps.
Protect Sensitive Data.

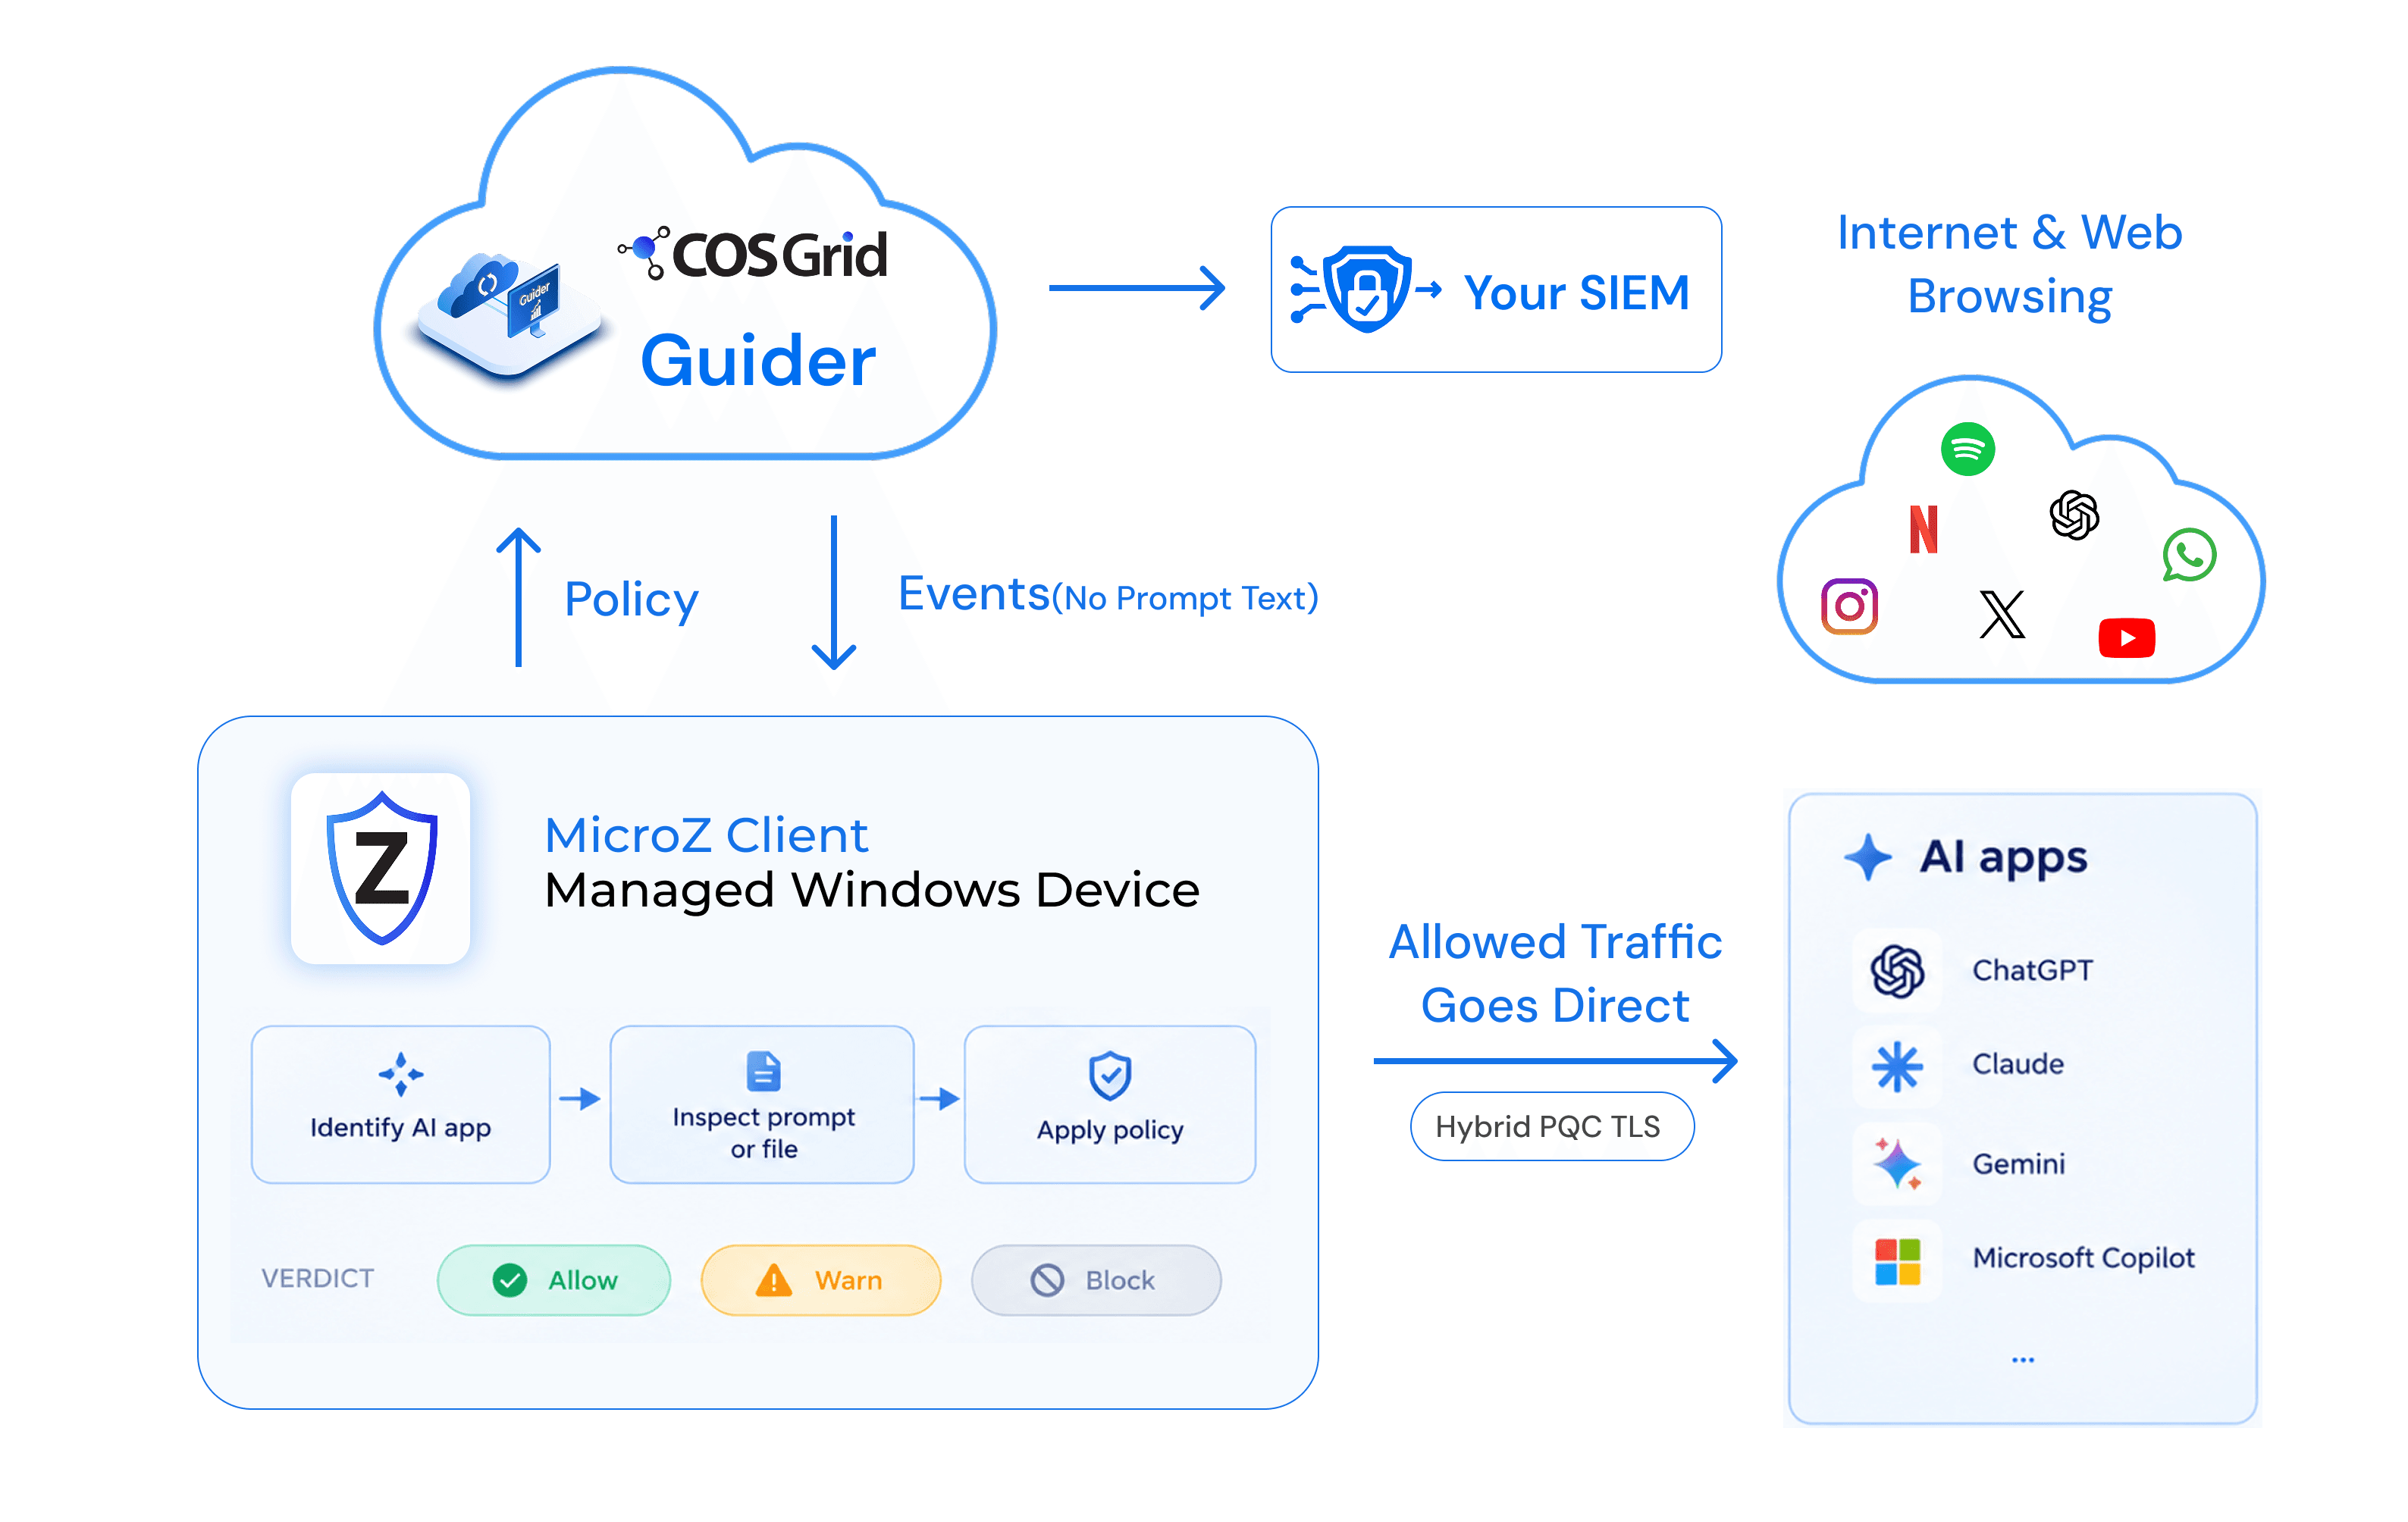
Discover AI apps on managed Windows devices, control approved apps, and protect sensitive data in prompts and uploads without storing prompt text.
Why teams switch to COSGrid TrustShield AI?

Discover AI Usage

Discover AI Usage

Find AI applications used on managed devices

Govern Application Access

Govern Application Access

Sanction, tolerate or block AI applications

Protect Sensitive Data

Protect Sensitive Data

Inspect supported prompts and file uploads

Secure and Control Enterprise AI Usage

Discover AI apps used across managed devices and control which are approved. COSGrid TrustShield AI helps security teams monitor AI usage and apply policies by app, user, and group. Protect sensitive data in supported AI prompts and file uploads with built-in Data Loss Prevention (DLP), without blocking all AI applications. Gain visibility into how employees use AI and reduce the risk of accidental data exposure. Enable safer AI adoption while maintaining control over enterprise data.

AI Adoption Is Moving Faster Than AI Governance

Unknown AI Usage icon

Unknown AI Usage

Employees may use AI apps without approval or clear security policies.
Sensitive Prompt Exposure icon

Sensitive Prompt Exposure

AI prompts may expose personal data, financial records, customer details, or credentials.
Unsanctioned AI Apps icon

Unsanctioned AI Apps

Identify approved AI tools and apply appropriate controls to unapproved apps.
Limited Audit Visibility icon

Limited Audit Visibility

Track who used AI, which device was involved, what activity occurred, and how policies responded.
How COSGrid TrustShield AI Works

Features

AI Governance and Data Protection at the Endpoint

Discover and Control AI Applications

  • Track AI apps, usage trends, data transfers, users and devices.
  • Classify apps as sanctioned, tolerated, unsanctioned or unreviewed.
  • Apply allow or block rules by app status, user or group.
  • Define custom AI applications and manage review decisions.
Discover and Control AI Applications

Differentiators

Practical AI Governance. Privacy-Conscious Protection.

Endpoint-Based Inspection

Endpoint-Based Inspection

  • Inspect supported AI traffic on managed Windows devices
  • No separate cloud AI gateway

Discover and Govern in One Console

Discover and Govern in One Console

  • Move from application inventory to status
  • Enforce policy through COSGrid Guider

Content-Aware DLP

Content-Aware DLP

  • Supported prompts and file uploads
  • Built-in recognizers and custom rules

Flexible Enforcement

Flexible Enforcement

  • Log, warn with typed justification, or block
  • Configured per application and policy

Privacy-Conscious Evidence

Privacy-Conscious Evidence

  • Original prompt text is not stored
  • Redacted excerpts and metadata-only mode

Organizational Data Patterns

Organizational Data Patterns

  • Indian identifiers, financial data, credentials
  • Custom patterns and keyword lists

Benefits

Enable AI Adoption With Greater Control

47
Plus custom patterns and keyword lists
Built-in data types
9
Ready to tailor to your policies
Ready-made DLP profiles
4
Sanctioned, tolerated, unsanctioned, unreviewed
Governance statuses
Better AI Visibility & Control
Discover AI apps, track usage, and govern applications by approval status
Reduced Data Exposure
Inspect supported AI prompts and file uploads for sensitive data
Accountable AI Usage
Apply warnings or blocks and record justifications for security reviews
Privacy & Investigation
Investigate AI activity using metadata and redacted events without storing original prompts

Use cases

AI Security for Enterprise Teams

Protect Sensitive Financial and Identity Data

Protect Sensitive Financial and Identity Data

Identify banking details, Indian identifiers, payment card data and other sensitive information in supported AI prompts and file uploads. Apply DLP policies to reduce accidental exposure of confidential financial and customer information.

Govern AI Usage Across the Organization

Govern AI Usage Across the Organization

Discover AI applications used across managed devices and classify them according to internal approval requirements. Monitor policy events and application activity to strengthen security oversight and support organizational compliance requirements.
Enforce AI Policies with Greater Control

Enforce AI Policies with Greater Control

Identify unreviewed and unsanctioned AI applications, manage approval status, and apply allow or block policies based on applications, users and groups. Review detected violations and recorded user justifications to support security investigations.

Enable Safer AI Adoption

Enable Safer AI Adoption

Gain visibility into AI tools used for coding, debugging and content generation. Inspect supported prompts and file uploads for exposed credentials, API keys, source code secrets and other configured sensitive data patterns while applying controls suited to your organization’s AI adoption needs.

COSGrid TrustShield AI

Have a question about COSGrid TrustShield AI?

questionWhat is COSGrid TrustShield AI?
arrow
COSGrid TrustShield AI is an AI usage control product that discovers supported AI applications, enables application governance and provides DLP for supported AI prompts and file uploads on managed Windows endpoints.
questionWhat is Shadow AI discovery?
arrow
Shadow AI discovery helps organizations identify AI applications being used by employees, including applications not yet formally reviewed or approved. TrustShield AI provides application inventory and usage information for supported applications on managed devices.
questionCan TrustShield AI block unsanctioned AI applications?
arrow
Yes. Administrators can assign governance statuses to AI applications and configure policies that target application status. Access can be allowed or blocked according to the applicable rule.