COSGrid CASB | Cloud Access Security Broker

Secure SaaS Access
with Endpoint Control.

Control SaaS access, corporate accounts and file transfers with inline Windows policies and direct cloud traffic.
Why teams switch to COSGrid CASB?

card.title

SaaS Visibility

Discover and filter supported SaaS applications

card.title

Account & File Control

Restrict personal accounts and file transfers

card.title

Centralized Policy

Distribute policies and review security events

Secure SaaS Usage With Granular Application-Level Controls

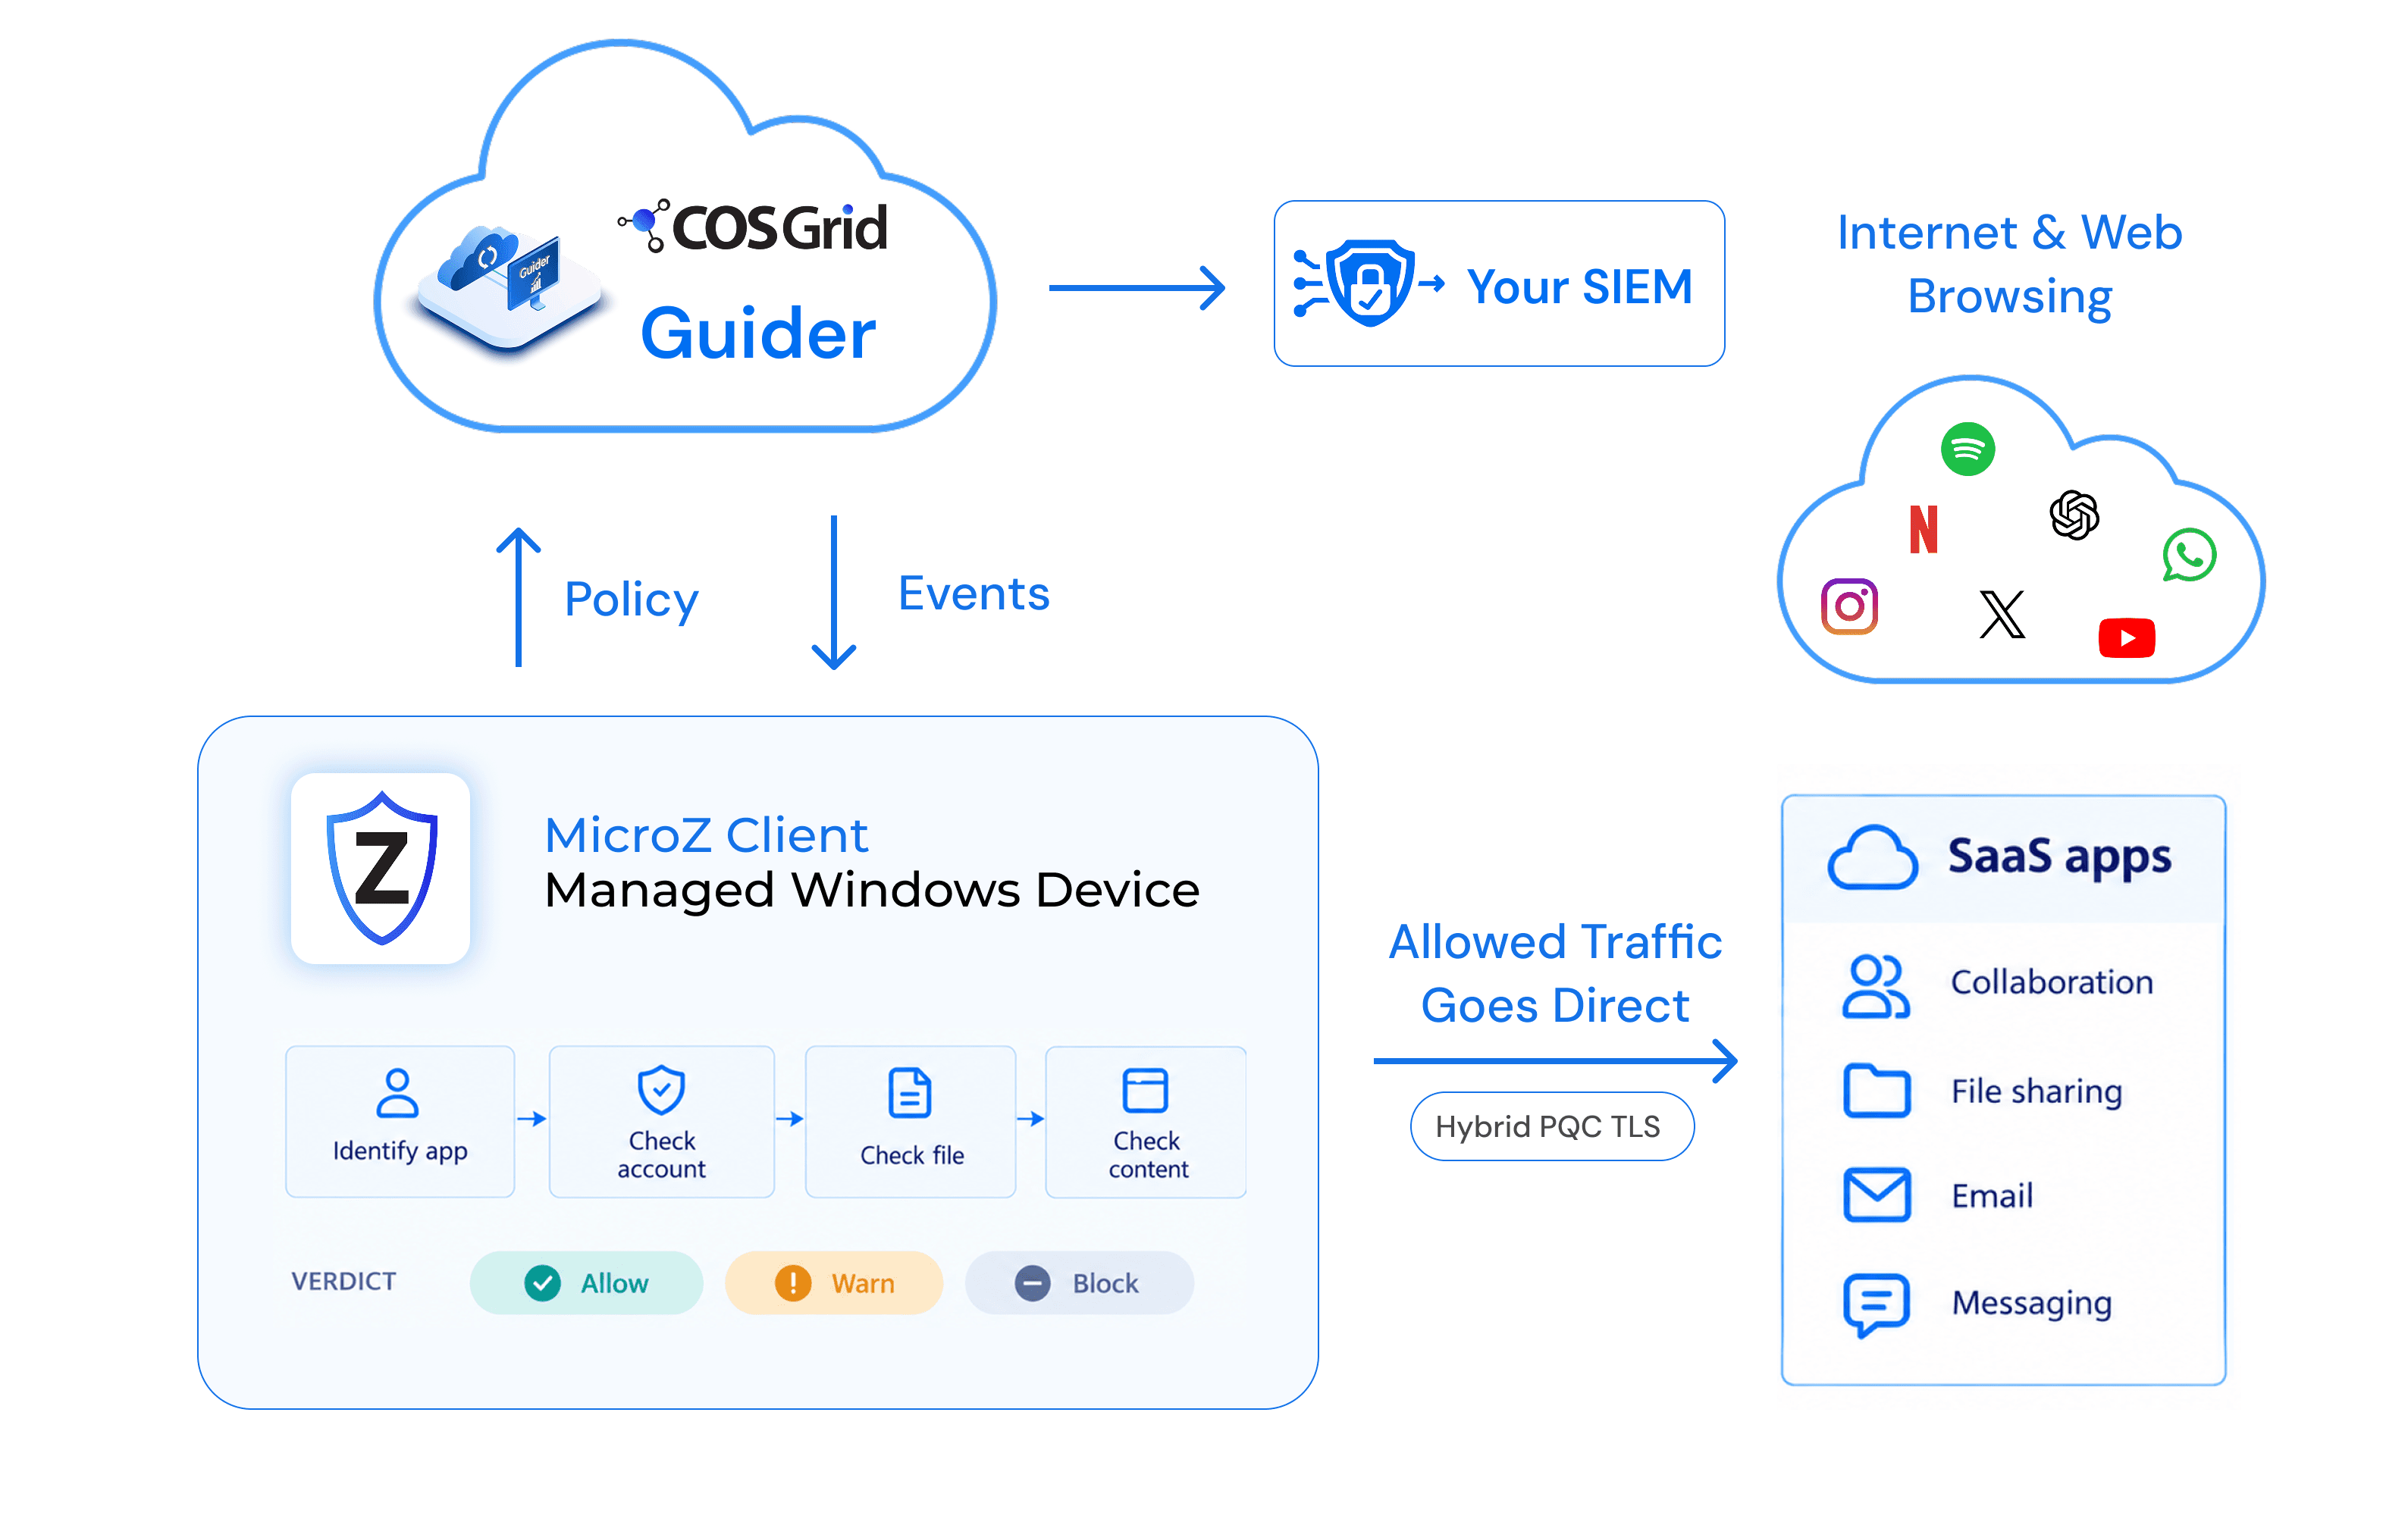
COSGrid CASB helps you control how employees use cloud applications, not just which ones they access. Granular policies cover application access, corporate-account usage and file transfers, enforced through device-side inline inspection on managed Windows endpoints while permitted traffic connects directly to SaaS destinations.

SaaS Adoption Needs More Than Application-Level Blocking

Account Control icon

Account Control

Restrict personal-account access while supporting approved corporate accounts.
File Transfer Restrictions icon

File Transfer Restrictions

Restrict unauthorized file uploads and downloads in supported SaaS applications.
SaaS Visibility icon

SaaS Visibility

Understand which cloud applications are accessed through managed endpoints.
Distributed Workforce Protection icon

Distributed Workforce Protection

Apply CASB policies on managed Windows devices across offices, homes and public Wi-Fi.

Device-Side Inline Inspection + Direct-to-SaaS Connectivity + Centralized Policy

Control SaaS without blocking it.

COSGrid CASB architecture

Features

What COSGrid CASB delivers

Understand Cloud Application Usage

  • Discover and filter supported SaaS applications accessed through managed endpoints.
  • Apply application-focused policies and review available application activity reporting.
Understand Cloud Application Usage

Differentiators

A Different Approach to SaaS Security

Device-Side Inline Inspection

Device-Side Inline Inspection

  • Enforce supported SaaS activity on managed endpoints
  • No third-party cloud proxy for inspected traffic

Direct-to-SaaS Connectivity

Direct-to-SaaS Connectivity

  • Permitted traffic goes straight to the SaaS destination
  • No third-party CASB proxy detour

Multiple Account-Control Methods

Multiple Account-Control Methods

  • Tenant validation, SSO enforcement and login-domain checks
  • Host blocking for personal editions

Granular File-Transfer Policies

Granular File-Transfer Policies

  • File-type, MIME-type and file-size restrictions
  • Beyond application-level allow or block decisions

Centralized Policy Distribution

Centralized Policy Distribution

  • Distribute policies through COSGrid Guider
  • Review available security events

Benefits

Secure SaaS Productivity With Greater Control

5
Tenant headers, subdomain, SSO, login domain, host blocking
Account-control methods
3
File type, MIME type and file size
File restriction types
Direct
SaaS Connectivity
Permitted traffic avoids a third-party proxy
Fewer Unauthorized Accounts
Distinguish corporate from personal accounts
Safer File Transfers
Restrict file types, MIME types and sizes
Better Visibility & Investigations
Understand SaaS usage and review policy decisions
Support for Distributed Workforces
Apply policies across office, home, branch and public Wi-Fi

Use cases

Built for enterprise SaaS security requirements

Control how employees access cloud applications and move files

Control how employees access cloud applications and move files

Apply corporate-account restrictions and supported file-transfer policies to help control how employees access cloud applications and move business files.

Manage SaaS usage and restrict file transfers

Manage SaaS usage and restrict file transfers

Manage SaaS application usage and restrict file transfers across supported collaboration, development, cloud-storage and productivity applications, with organizational account controls applied.
Maintain SaaS security policies wherever employees work

Maintain SaaS security policies wherever employees work

Maintain supported SaaS security policies on managed endpoints across office, home and remote working environments, with permitted traffic connecting directly to SaaS applications.

Align SaaS usage with organizational requirements

Align SaaS usage with organizational requirements

Apply corporate-tenant restrictions and application-specific policies to help align SaaS usage with organizational requirements.

COSGrid CASB

Have a question about COSGrid CASB?

questionWhat is COSGrid CASB?
arrow
COSGrid CASB is a Cloud Access Security Broker that helps organizations manage SaaS application usage through application visibility, corporate-account restrictions, file-transfer controls and centralized policy enforcement.
questionWhat is an inline CASB?
arrow
An inline CASB inspects application activity in the path of that activity so supported security policies can be enforced. COSGrid CASB uses device-side inspection on managed endpoints, with permitted traffic connecting directly to SaaS applications.
questionHow is COSGrid CASB different from a cloud-proxy CASB?
arrow
A cloud-proxy CASB routes application traffic through a cloud-based proxy for inspection. COSGrid CASB performs its documented inspection and enforcement on the managed endpoint while permitted application traffic travels directly to the SaaS destination.